
For years, IT asset disposition lived at the bottom of the priority list. Old laptops piled up in a storage closet. Servers got handed off to whoever would take them. Someone in IT handled it.
That era is over.
In 2026, retiring hardware without a documented, compliant process isn’t just sloppy – it’s a liability. The regulatory landscape has shifted fast, and most organizations haven’t caught up.
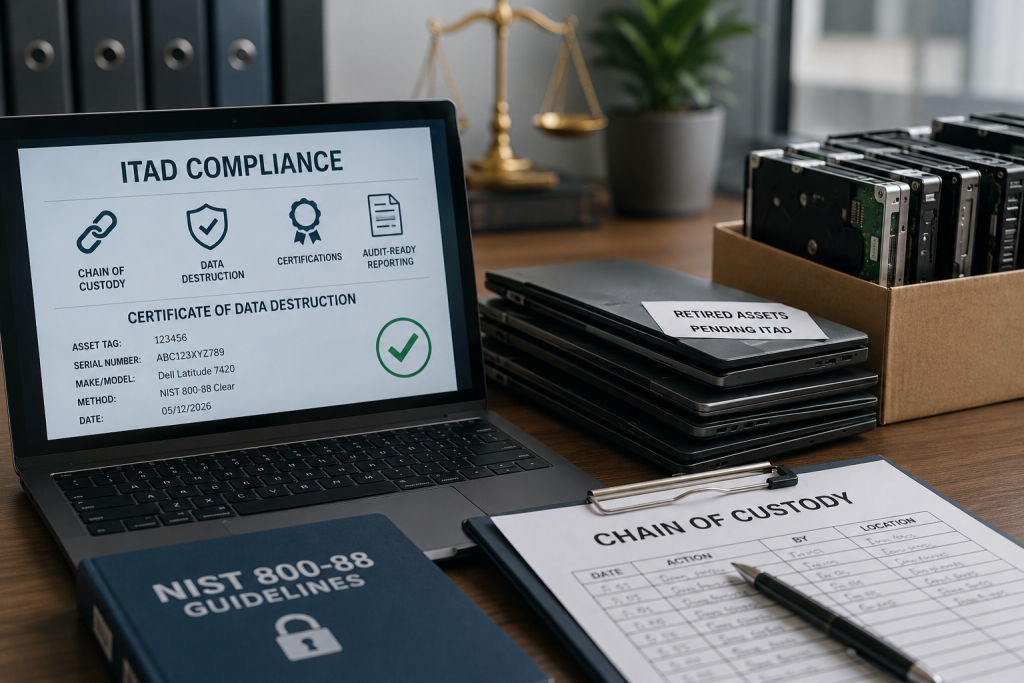
“Proper ITAD documentation – from chain of custody forms to certified data destruction records – is now a legal requirement, not just a best practice.”
The Rules Have Changed
Three converging forces have turned ITAD into a compliance issue:
1. State-level data privacy laws. Over a dozen U.S. states now have active data privacy legislation, and many of them include specific requirements around data destruction at end-of-life. “We wiped it” isn’t documentation. If you can’t produce a certificate of destruction tied to a serial number, you don’t have proof.
2. NIST 800-88. This federal standard for media sanitization has become the de facto benchmark that auditors, enterprise clients, and regulators expect to see. It’s not enough to delete files – the standard specifies sanitization methods by media type, and your ITAD partner should be able to show you exactly which method was applied to each device.
3. Basel Convention amendments. The updated rules on cross-border e-waste shipments now require prior informed consent and tighter documentation for any hardware moving across international borders. If your ITAD vendor is shipping retired equipment overseas – even for refurbishment – this applies to you.
And as of May 2026, the EU’s Digital Waste Shipment System (DIWASS) requires all notifications, routing, and regulator interactions for cross-border e-waste to flow through a single unified platform. If you do business in Europe or work with vendors who do, your chain of custody documentation needs to be audit-ready.
Why IT Teams Are Getting Caught Off Guard
Most IT teams still think of ITAD as a logistics problem – how to move equipment out the door efficiently. The legal team, meanwhile, assumes IT has it handled. That gap is exactly where exposure lives.
A data breach traced to improperly retired hardware isn’t just an IT incident anymore. Depending on the state and the data involved, it can trigger regulatory fines, breach notification requirements, and civil liability. The cost of a compliant ITAD program is a fraction of what a single incident can cost.
What “Compliant” Actually Looks Like
A compliant ITAD process isn’t complicated, but it has to be documented:
- Chain of custody tracking from the moment a device is decommissioned
- Certified data destruction using NIST 800-88-compliant methods, with certificates tied to individual assets
- R2v3 or e-Stewards certification from your ITAD vendor – these aren’t optional extras, they’re the baseline
- Audit-ready reporting so you can respond to a compliance inquiry without scrambling
The Bottom Line
If the last time your organization thought critically about IT asset disposition was when someone cleaned out the server room, it’s time to revisit it. The regulatory environment has changed. The risk has changed. And “we handed it off to someone” is no longer a defensible answer.
Castaway Technologies helps organizations retire hardware the right way – with full chain of custody documentation, certified data destruction, and reporting built for compliance teams, not just IT. If you want to talk through what your current process looks like and where the gaps might be, we’re happy to start that conversation.

